• Want to receive the latest contracting news and advice straight to your inbox? Sign up to the ContractorUK newsletter here. Every sign up will also be entered into a draw to WIN £100 Amazon vouchers!

Mac virus

5.00 star(s)
EDIT: here's an alternative take on manual removal, including updates for new variants that have come along since the instructions below first circulated. Also, the free ClamXAV app has been updated to deal with these bits of scumware.

For anybody who ends up installing one of these thingies on their Mac, it turns out getting rid of them is pretty simple. The main problem is that the Finder won't let you trash the application because it's in use by the running process(es), so:

  1. Locate the application (e.g. Mac Defender) in the Applications folder;
  2. Right-click (or Ctrl-click, or whatever you usually do to popup a context menu) and select "Show Package Contents";
  3. In the new Finder window that opens, select everything (Cmd-A is the quickest way) and send it to the Trash;
  4. Empty the Trash. If Finder complains that something is in use, select "Secure Empty Trash" from Finder's application menu;
  5. Restart (or, if you know what to look for, use Activity Monitor to terminate all relevant processes - generally, it's easier to restart);
  6. Find the application as in step 1; as it's now just an empty folder with a fancy icon, you should be able to send it to the Trash without any problem.

Sorted :)

You missed removing the Mac Protector entry from the startup items in your account:
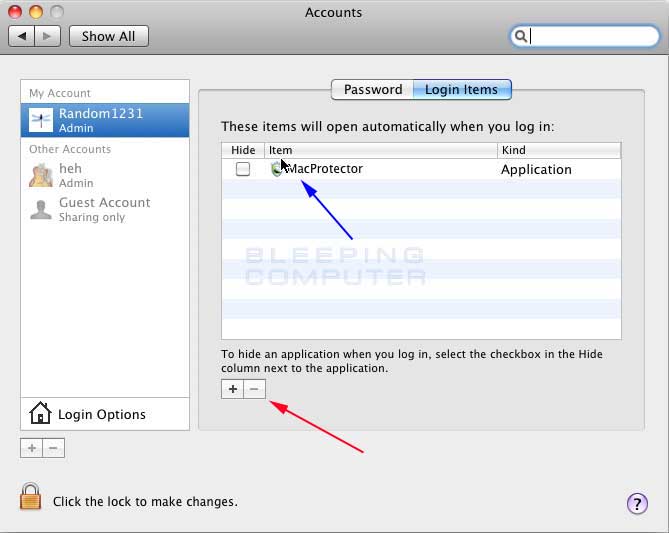
login-items.jpg


(I note that image shows the account as having Admin privilege. When will folks learn to set up and use a non-Admin account for general surfing????)

Once you've removed it from startup items, a simple logout and login should get rid of the process, and you will be able to delete it and empty Trash straight away.
 
Aha, I knew I'd read about this recently, but now I've found the reference:

DIY crimekit brings advanced malware to Mac OSX

A crimeware kit discovered over the weekend promises to bring a flood of advanced malware that steals passwords and other sensitive data from computers running Mac OS X.

The kit is being advertised as the Weyland-Yutani Bot in underground crime websites, where it's being sold for $1,000. The first ever crimeware kit for the Mac comes with the ability to grab data entered into Firefox, with the Chrome and Safari browsers soon to follow, according to Danish IT firm CSIS Security Group. The makers of the new DIY malware kit claim they are close to releasing versions that will work on iPads and Linux machines as well.
Oh, in case Linux users are feeling smug at the moment:

Note that last bit. It looks like it might be on the way to Linux platforms as well.
 
Aha, I knew I'd read about this recently, but now I've found the reference:

DIY crimekit brings advanced malware to Mac OSX

Note that last bit. It looks like it might be on the way to Linux platforms as well.

I don't think this is related to that, as it doesn't have the capabilities specified, and is more of a scam that tries to get users to enter credit card numbers in a web site rather than a virus, trojan, keylogger, or anything else. Microsoft Malware Protection Center reckon it's a derivative of WinWebSec.
 
:laugh to the bell end that neg repped me for this thread and didn't sign it :winker:

:rolleyes:

I'll rep you up. Just looked up an image on the Mac on google and got hit by this. As I don't normally use a Mac I was like WTF is this! And then remembered I saw this thread this morning. So good call Ruprect.

Is it just some google images or all?
 
I'll rep you up. Just looked up an image on the Mac on google and got hit by this. As I don't normally use a Mac I was like WTF is this! And then remembered I saw this thread this morning. So good call Ruprect.

Is it just some google images or all?

Some; it's a technique known as SEO poisoning, whereby you cause a domain to rank highly for some popular search terms and, once the Googlejuice is flowing your way, set it to redirect to the server with the evil crap. (You don't redirect when the Googlebot comes calling, obviously...)

EDIT: and, as explained in that Microsoft post I linked to up there, it's the server you're redirected to that detects whether you're on Windows or Mac and serves up the appropriate crap accordingly.
 
Last edited: 17:43
Anyone who enters their Admin credentials on an unsolicited Mac download deserves to be infected.

This isn't exploiting a Mac vulnerability, it's exploiting user stupidity.
 
Some; it's a technique known as SEO poisoning, whereby you cause a domain to rank highly for some popular search terms and, once the Googlejuice is flowing your way, set it to redirect to the server with the evil crap. (You don't redirect when the Googlebot comes calling, obviously...)

EDIT: and, as explained in that Microsoft post I linked to up there, it's the server you're redirected to that detects whether you're on Windows or Mac and serves up the appropriate crap accordingly.

It's my fault really. ATW said a bearded man was at the door. I then googled 'Jeremy Beadle' to find a suitable image to post. There he was dressed as a police officer, so I clicked it and lo and behold Mac Virus attack. Even in death the bearded twat is playing tricks! :eek
 

Advertisers

Back
Top





